Lemmy
  • Communities
  • Create Post
  • Create Community
  • heart
    Support Lemmy
  • search
    Search
  • Login
  • Sign Up
IanTwenty@piefed.social to Programming@programming.devEnglish · 3 days ago

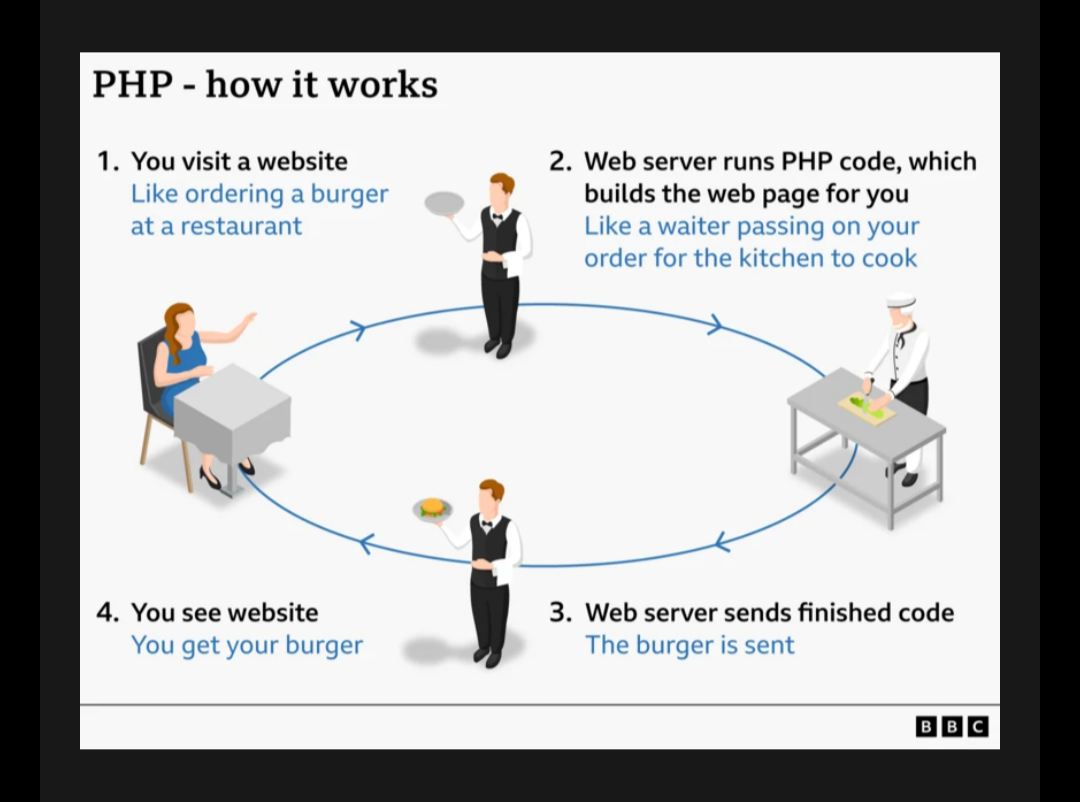
PHP: you get your burger

media.piefed.social

message-square
38
link
fedilink
124

PHP: you get your burger

media.piefed.social

IanTwenty@piefed.social to Programming@programming.devEnglish · 3 days ago
message-square
38
link
fedilink

https://www.bbc.co.uk/news/live/ckgel5xp2xv9t?post=asset%3Ac8185d02-3e14-4e83-9a99-6d3be2de04bd#post

alert-triangle
You must log in or # to comment.
  • expletivedeleted@lemmy.zip
    link
    fedilink
    arrow-up
    5
    ·
    1 day ago

    The cook should be represented as the database.

    Back in the 80’s, my brother “hacked” a pizza place because he knew how they wrote green olives and black olives on their ticket. He dated a girl who worked there for a stint.

    I don’t remember how it worked and he has since passed, but it was something with the order that he would list the toppings that would fuck up the cook, so the order always came out wrong and boom! Free pizza.

  • 0xDREADBEEF@lemmy.dbzer0.com
    link
    fedilink
    English
    arrow-up
    1
    ·
    1 day ago

    the person getting the burger actually has a user agent which fetches the burger for them. Its a food delivery app and the browser is doordash/uber eats etc. Instead of packets its human beings who read a screen and understand obligations.

  • Evotech@lemmy.world
    link
    fedilink
    arrow-up
    14
    ·
    2 days ago

    Step 5. you inject poison in your burger and send it back. Causing the cook to die and you take over as the owner of the restaurant

  • Blue_Morpho@lemmy.world
    link
    fedilink
    arrow-up
    60
    ·
    3 days ago

    How it should work for 99% of websites.

    https://motherfuckingwebsite.com/

    • NickwithaC@lemmy.world
      link
      fedilink
      English
      arrow-up
      11
      ·
      2 days ago

      CSS didn’t do shit wrong:

      http://bettermotherfuckingwebsite.com/

      • IphtashuFitz@lemmy.world
        link
        fedilink
        English
        arrow-up
        3
        ·
        1 day ago

        Can we get Samuel L. Jackson to read it for those with vision impairment?

      • Mikrochip@feddit.org
        link
        fedilink
        English
        arrow-up
        3
        arrow-down
        1
        ·
        1 day ago

        Love this one. Only thing I don’t get is why so many people can’t stand high contrast. Or even go so far as to say white background hurts their eyes. Black on white is just fine, thank you very much. And if it is too harsh, then I suspect that actually either one’s monitor is too bright, or - more likely - the environment they’re in is too dim.

    • Avicenna@programming.dev
      link
      fedilink
      arrow-up
      20
      ·
      edit-2
      3 days ago

      most people who have seen the old internet probably feel this rage

    • sem@piefed.blahaj.zone
      link
      fedilink
      English
      arrow-up
      12
      ·
      edit-2
      3 days ago

      Ublock blocks this for some reason

      EDIT turns out the reason is it appears to be infected with a botnet

      • Blue_Morpho@lemmy.world
        link
        fedilink
        arrow-up
        2
        ·
        2 days ago

        That’s weird. I did some digging and can’t find its name, ip, or hosting company servrex.com on any block list. I checked HaGezi on github based on your post.

        • sem@piefed.blahaj.zone
          link
          fedilink
          English
          arrow-up
          2
          ·
          2 days ago

          I used this https://github.com/hagezi/dns-blocklists#listlookup and searched https://motherfuckingwebsite.com/

          If you search the closed github issues, you’ll see more details for the url

          • Blue_Morpho@lemmy.world
            link
            fedilink
            arrow-up
            1
            ·
            2 days ago

            Which list? I searched the Multi Ultimate Full list and it wasn’t there.

            • ulterno@programming.dev
              link
              fedilink
              English
              arrow-up
              2
              ·
              1 day ago

              https://github.com/hagezi/dns-blocklists/issues/11017

              https://github.com/hagezi/dns-blocklists/issues/12026

              • Blue_Morpho@lemmy.world
                link
                fedilink
                arrow-up
                5
                ·
                edit-2
                1 day ago

                Well that’s even weirder. It is in a list labeled malicious/scammer/fishing.

                It absolutely isn’t any of those.

                Someone else claimed it pulls resources from a botnet but if you view source, that isn’t true.

                • sem@piefed.blahaj.zone
                  link
                  fedilink
                  English
                  arrow-up
                  1
                  ·
                  19 hours ago

                  Can ypu add to the github issue asking to review it?

                • ulterno@programming.dev
                  link
                  fedilink
                  English
                  arrow-up
                  1
                  ·
                  1 day ago

                  Well, I didn’t check its internals.

      • TrackenDaKracken@lemmy.world
        link
        fedilink
        arrow-up
        7
        ·
        3 days ago

        Not in Librewolf, at least. Ublock and Noscript enabled. Site still shows.

        • softotteep@pawb.social
          link
          fedilink
          English
          arrow-up
          9
          ·
          3 days ago

          You probably don’t have these filter lists enabled: 📒 HaGeZi - Multi PRO mini 🔐 HaGeZi - Threat Intelligence Feeds - Mini

        • Nocklusamigos@lemmy.world
          link
          fedilink
          arrow-up
          1
          arrow-down
          2
          ·
          2 days ago

          Adguard blocks it. Adguard usually is more trustworthy

  • Dry_Monk@lemmy.world
    link
    fedilink
    arrow-up
    1
    arrow-down
    1
    ·
    1 day ago

    4

  • MidsizedSedan@lemmy.world
    link
    fedilink
    arrow-up
    4
    ·
    2 days ago

    Dam, I guess I was a programmer at KFC, and I didn’t even know it…

  • username_1@discuss.tchncs.de
    link
    fedilink
    arrow-up
    16
    ·
    3 days ago

    Wow! That’s why I love analogies – in most cases they don’t make any sense especially if you are not a specialist in the theme.

    • Ephera@lemmy.ml
      link
      fedilink
      arrow-up
      2
      ·
      3 days ago

      Well, they do have some prose in the link that OP also posted, but yeah, it is a bit rough, especially if you’re trying to understand the vulnerability…

      • tourist@lemmy.world
        link
        fedilink
        arrow-up
        6
        ·
        3 days ago

        holy fuck

        70% of websites are running PHP?

        are they sure?

        Am I going to find a php binary in a node_modules directory

        • NoDignity@lemmy.world
          link
          fedilink
          English
          arrow-up
          3
          ·
          2 days ago

          I kinda buy the 70% claim, mostly because lots of old CMS systems are built using PHP some of which are still extremely popular like wordpress.

          • adarza@lemmy.ca
            link
            fedilink
            English
            arrow-up
            5
            ·
            1 day ago

            over half of that 70% is just wordpress.

  • one_old_coder@piefed.social
    link
    fedilink
    English
    arrow-up
    14
    ·
    3 days ago

    Wait till you learn about this new CGI thing, you’ll be amazed about what it can do: https://en.wikipedia.org/wiki/Common_Gateway_Interface

    • OpenStars@discuss.online
      link
      fedilink
      English
      arrow-up
      5
      ·
      3 days ago

      I doubt it will cook burgers for you though 😕 😔 🍔🍴🤤

      For some reason I am hungry all of a sudden…

  • twinnie@feddit.uk
    link
    fedilink
    arrow-up
    6
    ·
    3 days ago

    Most of my experience with PHP is from pen testing so most of my orders look something like <?$_GET[0]?>

  • TootSweet@lemmy.world
    link
    fedilink
    English
    arrow-up
    8
    arrow-down
    1
    ·
    3 days ago

    Why is everybody talking about PHP lately? Am I out of the loop?

    • username_1@discuss.tchncs.de
      link
      fedilink
      arrow-up
      15
      arrow-down
      1
      ·
      3 days ago

      They fixed a bunch of vulnerabilities there which were known for years but neither hackers nor PHP developers cared much until recently.

      • UnfairUtan@lemmy.world
        link
        fedilink
        arrow-up
        3
        ·
        3 days ago

        Wait it was known!? They didn’t just discover it and fixed it quickly?

        • chameleon@fedia.io
          link
          fedilink
          arrow-up
          16
          ·
          3 days ago

          It’s not a quick or easy fix. The patch is a 10000 line nightmare. No really it’s actually 10k. A lot of that is test code, but there are also significant changes to deep engine internals.

          PHP did really really bad memory limit handling. Now it’s only really bad.

          • UnfairUtan@lemmy.world
            link
            fedilink
            arrow-up
            3
            ·
            3 days ago

            Wow scary fix, I’m guessing we’re going to be seeing a few new patches really soon fixing bugs created by this latest version

        • username_1@discuss.tchncs.de
          link
          fedilink
          arrow-up
          11
          arrow-down
          1
          ·
          3 days ago

          No, they chewed snots for years because there wasn’t a trivial and straightforward fix and exploit looked too “theoretically possible”. But some time ago(months? year?) some company showed them a working exploit, so they started to think how to actually fix the problem. All that time they kept all in secret so hackers wouldn’t know. But the fix had leaked, letting hackers to figure out what was the vulnerability in the first place, so snot-chewing was replaced with running-and-screaming. By now everything is fixed for those who cared to update\recompile. Something like that.

          • UnfairUtan@lemmy.world
            link
            fedilink
            arrow-up
            1
            ·
            3 days ago

            Thanks, makes sense!

    • jokro@feddit.org
      link
      fedilink
      arrow-up
      7
      ·
      3 days ago

      To add what the others said, yesterday morning there was news that every php version is vulnerable but the fixes were published very late in the day (or whenever depending on timezone) thus there was a 8+hours of unceartiny and fear for administrators. A lot of websites shut down due to that.

Programming@programming.dev

programming@programming.dev

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !programming@programming.dev

Welcome to the main community in programming.dev! Feel free to post anything relating to programming here!

Cross posting is strongly encouraged in the instance. If you feel your post or another person’s post makes sense in another community cross post into it.

Hope you enjoy the instance!

Rules

Rules

  • Follow the programming.dev instance rules
  • Keep content related to programming in some way
  • If you’re posting long videos try to add in some form of tldr for those who don’t want to watch videos

Wormhole

Follow the wormhole through a path of communities !webdev@programming.dev


Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 712 users / day
  • 1.96K users / week
  • 3.27K users / month
  • 8.08K users / 6 months
  • 2 local subscribers
  • 29K subscribers
  • 3.71K Posts
  • 47.8K Comments
  • Modlog
  • mods:
  • snowe@programming.dev
  • Ategon@programming.dev
  • UlrikHD@programming.dev
  • bugsmith@programming.dev
  • Spyro@programming.dev
  • BE: 0.19.14
  • Modlog
  • Instances
  • Docs
  • Code
  • join-lemmy.org